See CVEs and CIS drift alongside APM and cost.
Powered by Kubescape, vulnerability and CIS Benchmark posture live in the same platform as APM and cost, not a separate security dashboard you check on a different day.
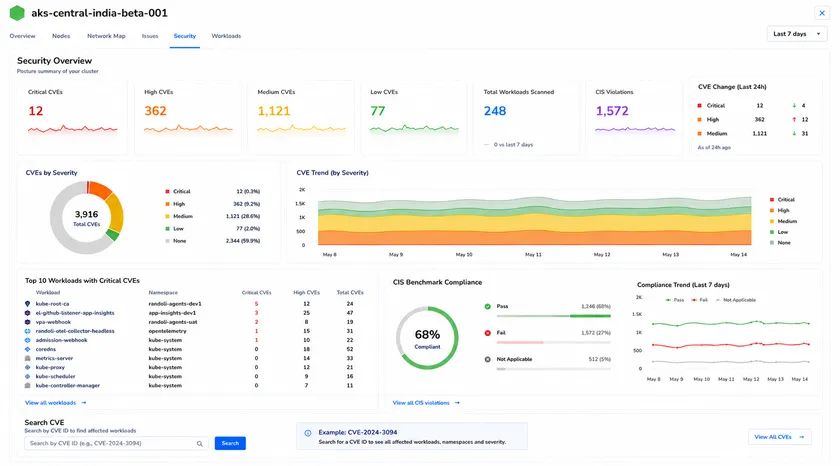
Powered by Kubescape, running in the same data plane that collects your other signals.
Compliance posture scored per workload, namespace, and cluster.
Vulnerability and CIS posture in the same platform as APM and cost, not a separate tool.
Drill down from cluster-wide exposure to the specific workload driving it.
Alerts on sudden spikes in critical or high-severity CVEs, through the same channels as the rest of your alerting.
Get paged when critical exposure spikes, not just when it exists.
A long static list of CVEs is easy to ignore. Randoli watches for sudden increases in critical and high-severity CVEs across your workloads and raises it as an anomaly, through the same alerting your team already uses for everything else.
See how it fits with the rest of the platform in Observability for Kubernetes and Cost Management for Kubernetes.